Qian Lou
Bio
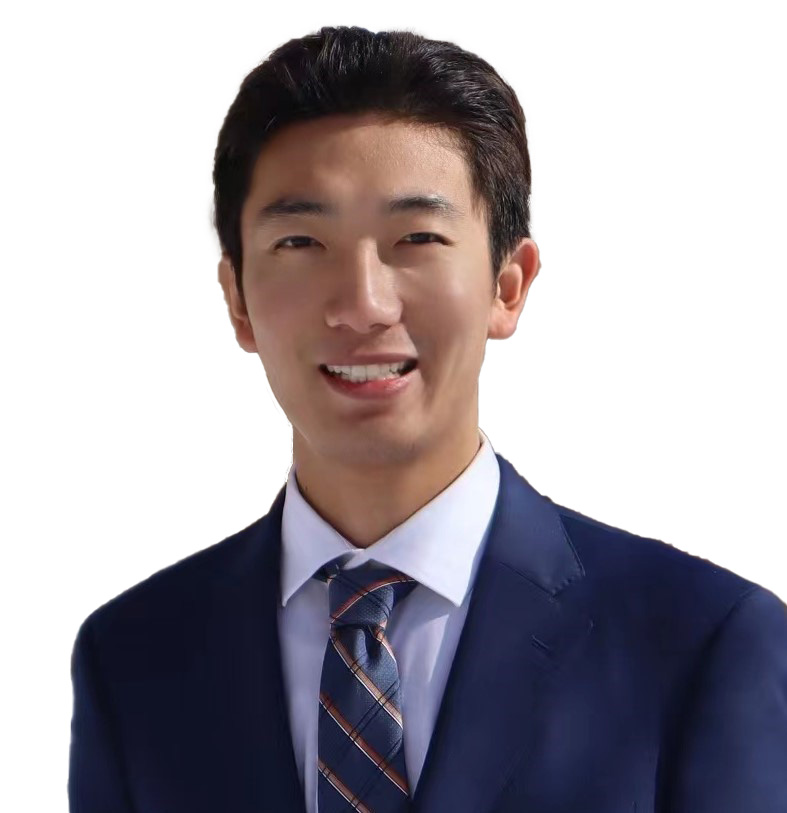
Qian Lou is a researcher and professor at the University of Central Florida, serving as Principal Investigator on projects supported by NSF, NIH, and Amazon. His research develops AI infrastructure for secure and private computation, private verification, and privacy-preserving learning and data synthesis. He has developed new cryptographic primitives and compilers that enable new AI applications, and develops AI agents for cryptanalysis and cryptographic programming. His goal is to unlock the value of sensitive and distributed data while expanding AI's capabilities and applications.
He received the NSF CAREER Award in 2026. His work appears in leading AI, security, and systems venues, including NeurIPS, ICML, ICLR, IEEE S&P, and DAC. Before joining UCF, he was a Senior Research Scientist at Samsung AI Center in Mountain View. His work has received a Samsung Research Best Paper Award and Best Paper Finalist honors at PACT and ICCAD.
Research
How can AI infrastructure enable secure and private computation, private verification, and private learning and data synthesis?
Driven by this question, our research aims to unlock sensitive data without exposing it, enable verification over private data, and unleash the potential of underused “dark data” and distributed data. Through these advances, we aim to expand AI's capabilities, scale its deployment, and enable new applications.
We pursue this goal through two connected directions: Crypto for AI and AI for Crypto. Crypto for AI pursues native-complexity, general-purpose, and verifiable homomorphic encryption (nuvFHE) primitives and sub-linear zero-knowledge proofs for general matrix multiplication (redZKP), and develops compilers such as CipherFlow. Our compiler dynamically and automatically maps AI computation graphs from frameworks such as PyTorch to secure computation graphs using fully homomorphic encryption (FHE), nuvFHE, secure multiparty computation (MPC), and related techniques. These efforts support secure applications in AI training, inference, verification, and data synthesis. We also combine cryptographic foundations with complementary techniques, including trusted hardware and differential privacy. AI for Crypto develops agents for cryptanalysis and for generating and optimizing cryptographic programs under explicit functional and security checks.
I. Crypto for AI
We co-design cryptographic primitives, compilers, and applications to make private computation and verification practical for AI.
Primitives for private computation and verification
We pursue native-complexity, general-purpose, and verifiable homomorphic encryption through nuvFHE, alongside redZKP for sub-linear zero-knowledge proofs for general matrix multiplication. Our foundational work addresses complementary challenges:
- Efficient encrypted computation. SHE (NeurIPS 2019) co-designs model representations and encrypted arithmetic to reduce computation costs. [Paper]
- General-purpose encrypted operations. Universal-BGV (IEEE S&P 2026) connects arithmetic and comparison within one FHE scheme. [Paper] [Code]
- Verifiable encrypted computation. DataSeal (IEEE S&P 2025) adds checks for the correctness of supported encrypted computations. [Paper]
- Private verification. zkVC (DAC 2025) accelerates zero-knowledge proofs for matrix computations while protecting the server's private information. [Paper] [Code]
Compilers connecting AI models to secure execution
Our compiler research connects AI computation graphs with secure execution, coordinating model transformations, cryptographic protocols, and hardware choices.
- CipherFlow (NeurIPS 2026). Plans hybrid secure inference using model dependencies and measured hardware and network costs, reducing redundant planning work while coordinating protocol and placement choices. [Publication]
- HEMET (ICML 2021) and SAFENet (ICLR 2021). Establish model co-design techniques that reduce protected inference costs while accounting for accuracy. [HEMET paper] [SAFENet paper]
Applications enabled by privacy and verification
We use these foundations to support private learning, inference, verification, and data synthesis. Where appropriate, we combine cryptographic protection with trusted hardware and differential privacy.
- Private learning. DictPFL (NeurIPS 2025) supports federated learning with encrypted gradients. [Paper]
- Private inference. SecureRoute (DAC 2026) protects adaptive model selection and inference using MPC. The public preprint is titled SecureRouter. [Paper]
- Private data synthesis. FHAIM (ICML 2026) combines encrypted computation with differential privacy to protect source data and the release of synthetic data. [Paper]
- Healthcare AI. Our ongoing NIH R01 develops evidence-grounded collaborative agents for bacterial infection decision support, motivating protected access to sensitive institutional data alongside clinical validation and clinician oversight. [Funding]
II. AI for Crypto
We develop AI agents for cryptanalysis and for generating and optimizing cryptographic software, with functional and security requirements guiding the process.
- Cryptographic programming. FHE-Coder (ICLR 2026) combines task formalization, relevant documentation, and external checks to generate functional and secure FHE programs. [Paper] [Benchmark & project]
- Cryptographic optimization (ongoing). We study agents that improve implementations using execution measurements while preserving functional and security requirements.
- Cryptanalysis (ongoing). We investigate AI-assisted analysis of cryptographic constructions and implementations.
Connecting the two directions. Protected AI applications reveal performance bottlenecks and implementation needs. Our longer-term goal is to use this evidence to guide AI-assisted cryptographic development, with proposed improvements undergoing validation before returning to the secure computing stack.
Selected Publications
* indicates students and staff under my supervision. Complete publication list.
[NeurIPS 26] CipherFlow: Hardware-Aware Compiler Framework for Low-Latency Hybrid Secure Inference |
[ICML 26] FHAIM: Fully Homomorphic AIM For Private Synthetic Data Generation |
[S&P 26] Efficient Arithmetic-and-Comparison Homomorphic Encryption with Space Switching |
[DAC 26] SecureRoute: Input-Adaptive Encrypted Routing for Efficient and Accurate MPC-Based Transformer Inference |
[ASPLOS 26] ReliaFHE: Resilient Design for Fully Homomorphic Encryption Accelerators |
[ICLR 26] FHE-Coder: Secure Agentic Code Generation for Fully Homomorphic Encryption |
[NeurIPS 25] DictPFL: Efficient and Private Federated Learning on Encrypted Gradients |
[DAC 25] zkVC: Fast Zero-Knowledge Proof for Private and Verifiable Computing |
[ICLR 25] CipherPrune: Efficient and Scalable Private Transformer Inference |
[S&P 25] DataSeal: Ensuring the Verifiability of Private Computation on Encrypted Data |
[ICML 21] HEMET: A Homomorphic-Encryption-Friendly Privacy-Preserving Mobile Neural Network Architecture |
[ICLR 21] SAFENet: A Secure, Accurate, and Fast Neural Network Inference |
[NeurIPS 19] SHE: A Fast and Accurate Deep Neural Network for Encrypted Data |
Open Source
- FHE-Coder: benchmark and project resources for agentic FHE programming.
- Universal-BGV: FHE arithmetic and comparison through space switching.
- zkVC: zero-knowledge proofs for private and verifiable computing.
- UCF-Lou-Lab-PET: our group's privacy-preserving computing and AI repositories.
People
This research brings together students and collaborators working on cryptographic computing and AI systems. Selected student contributors include:
- Mayank Kumar: FHE-Coder and FHAIM.
- Jiaqi Xue: FHE-Coder, DataSeal, and private learning.
- Hedong Zhang: CipherFlow and secure inference compilation.
- Yukuan Zhang: SecureRoute and private model routing.
- Erwin Eko Wahyudi (with Yan Solihin): Universal-BGV.
Collaborators across these projects include Mengxin Zheng, Yan Solihin, Lei Jiang, Paulo Barreto, Martine De Cock, and Sikha Pentyala. Meet the full research group.
Funding & Recognition
Research and education support spans secure computing, AI systems, healthcare AI, and workforce development.
Research & Education Funding
PI: Principal Investigator. Co-PI: Co-Principal Investigator.
- 2026Amazon Research Award (PI)
Trainium-native controller-guided compression and alignment-preserving post-training.
$250K in AWS credits. [Program] - 2026NIH/NIAID R01 (PI)
Collaborative AI Agents for Bacterial Infections: A Knowledge-Grounded Framework to Support Clinical Practice Guidelines and Clinical Decision-Making. [Program]
- 2026NSF CyberAI Scholarship for Service (SFS) (Co-PI)
CyberAI SFS: Educating Florida's Federal CyberAI Workforce for Secure AI in Space, Defense, and Modeling & Simulation. [Award 2622846]
- 2026NSF CAREER (PI)
Scalable, General-Purpose, and Automated Secure Computing for AI Infrastructure. [Award OAC-2544047]
- 2026NSF Research Experiences for Undergraduates (REU)
Support for undergraduate research experiences. [Program]
- 2025NSF Secure and Trustworthy Cyberspace (SaTC) (PI)
Collaborative Research: Privacy-Preserving Synthetic Data Generation. [Award CCF-2523407]
- 2025Department of Defense Pathfinder Program (PI)
LLM Security Testing.
- 2024NSF CISE Core / CSR Small (PI)
System Support for Fast, Scalable, and Verifiable Fully Homomorphic Encryption. [Award CNS-2413232]
- 2024Arctic Wolf Networks, Inc. (Co-PI)
Industry research support.
Honors & Recognition
- 2026: NSF CAREER Award. [UCF feature]
- 2026: ASEM-FL Rising Star Award. [Program]
- 2022: Samsung Research Best Paper Award.
- 2020: Best Paper Finalist, PACT.
- 2018: Best Paper Finalist, ICCAD.
Selected Service & Outreach
- DAC 2026 SPGAI Workshop Chair. Secure and Private System Design for Generative & Agentic AI. [Workshop]
- Program committee service for CCS 2026 and NDSS 2026, and technical program committee service for DAC.
- UCF research feature. Advancing AI security through the NSF CAREER program. [Read]